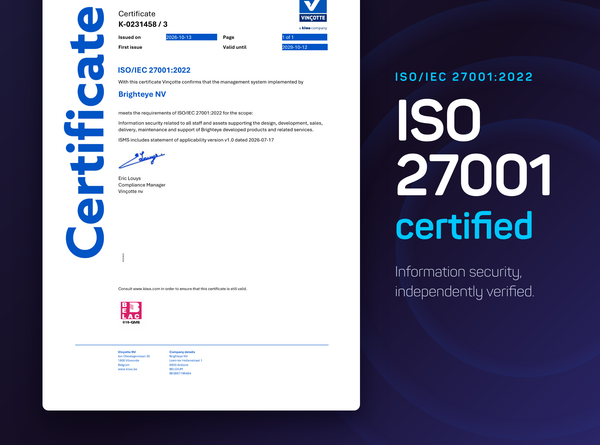
That is why we are pleased to announce that Brighteye is now officially certified to ISO/IEC 27001:2022, the international standard for information security management.
What ISO/IEC 27001 covers
ISO/IEC 27001 defines how an organisation sets up, runs and continuously improves an information security management system (ISMS). It is more than a technical checklist. The standard asks a company to identify its information security risks, decide how to treat them and prove that those measures work in practice.
The 2022 version contains 93 controls in four themes: organisational, people, physical and technological. They cover access management, secure software development, supplier management, incident response, business continuity and more.
Independently verified, across the full lifecycle
Our certificate was issued by Vinçotte, a BELAC-accredited certification body, after an independent audit of our ISMS. Two things matter here.
First, the scope. It covers information security for all staff and assets supporting the design, development, sales, delivery, maintenance and support of Momentum and related services. It is not limited to one department or one hosting environment.
Second, it is not a one-off snapshot. Annual surveillance audits check that the system keeps working, until recertification in 2029.
Why this matters for manufacturers
The NIS2 directive makes supply chain security an explicit part of a company’s own cybersecurity obligations. Many food producers and industrial manufacturers now fall within its scope and must show that they manage the risks introduced by their suppliers, including software suppliers.
In Belgium, ISO/IEC 27001 is one of the recognised frameworks for demonstrating that level of control. Working with a certified MOM partner means you do not have to assess our security practices from scratch. An independent party has already verified them.
To be clear, our certification does not make your organisation NIS2 compliant. It gives you solid, auditable evidence for one important part of the picture: the security of a critical supplier.
Built for long-term partnerships
Momentum is designed to grow with you: module by module, line by line, site by site, often over many years. That kind of partnership depends on trust that goes beyond functionality. ISO/IEC 27001 makes that trust measurable.
Thank you to everyone at Brighteye who helped make this happen.
Want to know more?
Want to know how Momentum handles information security in your environment, or need documentation for your own supplier assessment? Contact our team.